What is account takeover (ATO) and how to stop it

Account takeover (ATO) is when an attacker gets into an account they don't own and uses it for fraud. This guide explains how ATO becomes scams on social media, how credentials get compromised, and the layered defenses that stop it.
Account takeover (ATO) is when an attacker gets into an account that belongs to someone else, usually with stolen or phished login details, and uses it as if they were the owner. You prevent it with unique passwords, multi-factor authentication, phishing awareness, protected devices and round-the-clock monitoring of your accounts.
Hackers take over accounts for all sorts of reasons: scamming users, distributing ransomware and spreading political messages. Social media hacks keep making headlines, and each one damages brand reputations and costs users money.
The most recent high-profile incidents show no one is safe. From Samsung and Nasdaq to the NBA and NASCAR, even the biggest organizations with massive security budgets fall victim to account takeovers.
In this post, we'll cover what account takeovers are, how they turn into fraud, how credentials get compromised, who gets targeted, and the practical steps you can take to protect your organization. If you want a step-by-step plan, see our account takeover fraud prevention guide. If you're comparing tools, see our list of the best account takeover protection software.
What is account takeover (ATO)?
Account Takeover (ATO) is an attack where cybercriminals take ownership of online accounts using different methods like stolen passwords and usernames, phishing, and malware.
Another common method is to buy lists of credentials on the dark web that were most likely obtained through social engineering, data breaches or phishing.
Attackers test these credentials using bots across sites like finance, retail, eCommerce, and social media to find valid logins. Once inside, they can steal information, make fraudulent transactions, hold them for ransom, or use the account for further attacks.
What is account takeover fraud?
Account takeover fraud is what happens after an attacker gets into an account: they use it to steal money, data or the trust the owner has built. Banks and online stores see it as unauthorized transactions. On social media it usually looks like scams posted from an account people already trust.
The numbers show how costly this has become. The FBI received more than 5,100 complaints about account takeover fraud that started with attackers impersonating financial institution support in 2025, with reported losses over $262 million.1 Americans also reported losing $2.1 billion to scams that started on social media in 2025.2
How account takeover becomes fraud on social media
A hijacked brand or creator account is valuable because followers believe what it posts. Attackers use that trust in a few common ways:
- Scams posted from a trusted account: fake offers, fake investment tips and fake support messages reach followers who have no reason to doubt them. Our guide to social media scams covers the most common types.
- Fake giveaways: a "flash giveaway" post sends fans to a fake checkout or form that collects card details and personal information.
- Crypto scams: attackers post a fake token launch or "send crypto, get double back" promotion, as in the McDonald's Instagram hack and a pro golfer's hijacked account.
- Phishing DMs: the attacker messages followers, customers and partners from the real account with a link to a fake login page, which can lead to more stolen accounts.
How credentials get compromised
Credential compromise means someone other than the owner has the login details for an account. It's the step that comes before almost every takeover. The most common routes are:
- Phishing: a fake email, DM or login page tricks someone into typing their password and sometimes their 2FA code.
- Reused passwords: a password leaked in one breach gets tried on other sites, which is called credential stuffing.
- Infostealer malware: malicious software on a device quietly copies saved passwords, browser data and other login details. A May 2025 joint advisory from the FBI and CISA describes infostealers that spread through phishing emails, fake CAPTCHA pages and fake software downloads, and that can also steal multifactor authentication details.3
- Session theft: malware or a fake login page copies the session token that keeps you logged in, so the attacker can skip the password and the 2FA prompt.
We explain each of these in more detail below, along with the defenses that work against them.
What types of organizations do ATO attacks target?
Financial institutions used to be the main focus for account takeover (ATO) attacks. But today, any organization with online accounts is at risk.
Attackers now go after diverse sectors, depending on what they can get out of it. For example:
- Financial services and eCommerce are still high on the hit list. Hackers hijack accounts to make fraudulent purchases using stored payment details or steal cryptocurrency.
- Public sector, healthcare, and education are frequently targeted for their valuable personally identifiable information (PII), which can be used for identity theft, insurance fraud, or credit fraud.
- Any organization with high value user accounts risks having that data stolen and sold on dark markets, or used as entry points for ransomware.
How account takeovers happen
Understanding how account takeovers work is relatively simple but it can get complicated depending on how it's done. Here are the most common ways hackers use to take over accounts:
1) Theft of login credentials via a data breach
Stealing login credentials via data breaches typically is done through exploiting vulnerabilities in systems or human behavior to gain unauthorized access to databases where sensitive user information like usernames, email addresses and passwords is stored.
Data breaches are a huge problem. Billions of passwords have been exposed in data breaches over the years, which gives attackers a huge supply of logins to test.
Here's how these types of attacks are typically done: Hackers first identify a target like a website, application, or service with user accounts. They then use techniques like:
- Exploiting vulnerabilities in web applications (SQL injection, broken authentication, etc.)
- Compromising servers through unpatched software or misconfigurations
- Social engineering attacks against employees with database access
- Insider threats from malicious employees
- Third-party vendor compromises that affect connected systems
Once inside, the attacker tries to access the database storing user credentials and if the data is unencrypted or poorly encrypted, it's an easy win.
The security of this data depends heavily on how it was stored:
- Plaintext passwords (worst case) are immediately usable.
- Hashed passwords require cracking but are often vulnerable to rainbow table attacks or brute force.
- Properly salted and hashed passwords are much more difficult to crack but not impossible.
After that, the attacker copies the login data and transfers it to a remote server they control. If passwords are hashed, attackers use dictionary attacks, rainbow tables or brute force attacks.
Stolen credentials are then used directly (if the breach is recent and the user hasn't changed their password), tested on other services (credential stuffing), and often sold on the dark web.
2) Brute force credential cracking

Brute force credential cracking is a trial-and-error hacking method used to crack passwords, login credentials, and encryption keys. The name "brute force" comes from attackers using excessively forceful attempts to gain access to user accounts.
Despite its simplicity, it remains a significant security threat, and most hacking-related breaches involve either brute force attacks or compromised credentials, according to one industry analysis.
The attack process begins when: The attacker gets a list of usernames or emails from a breach or scraped data. They then use a script or bot to systematically attempt passwords for each account.
There are different variations to do it like simple brute force (try all possible character combinations), dictionary attacks (list of common or likely passwords), and credential stuffing (use known username/password pairs from other breaches on different sites).
3) Phishing for login information
Phishing is one of the biggest cybersecurity threats there is, and an annual breach cost report ranks it among the most common ways breaches begin, with each breach costing organizations millions.
What's worse is that the scale of this threat continues to grow, with millions of phishing attacks detected worldwide every year.
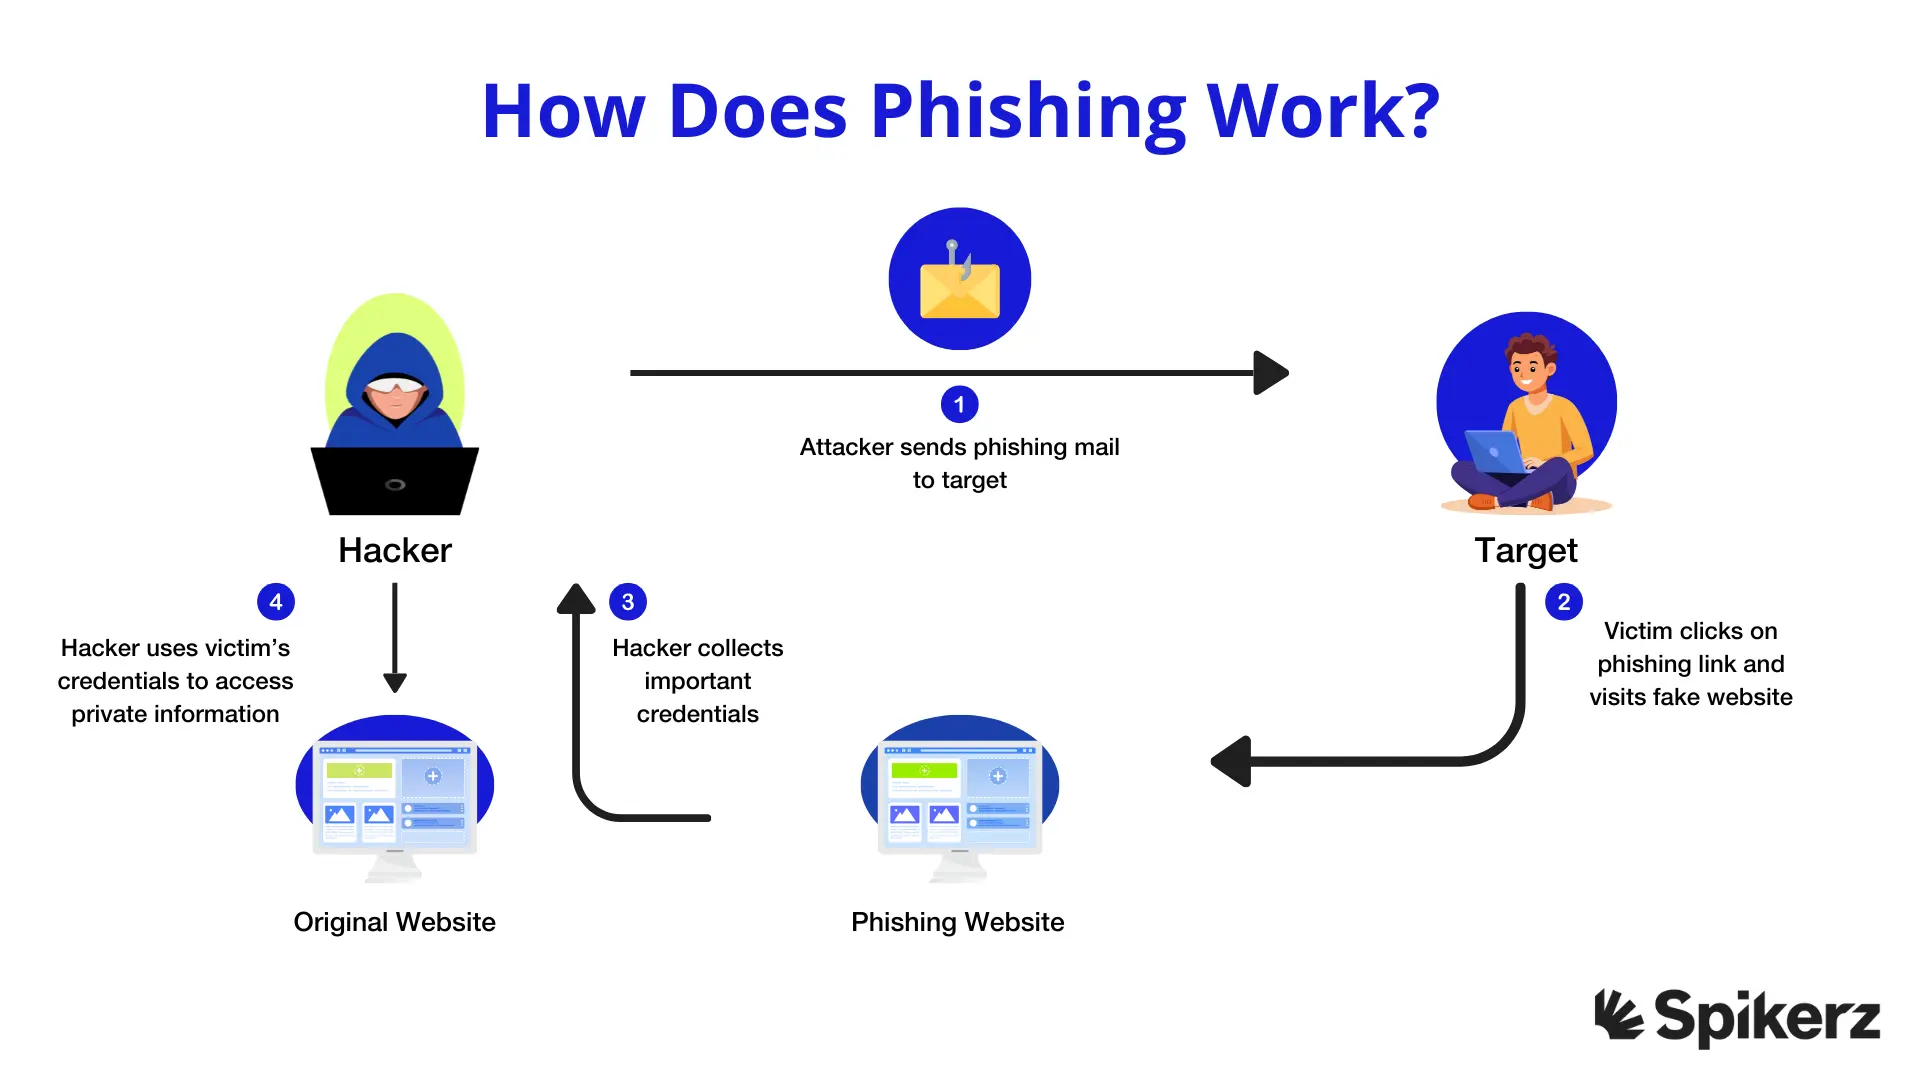
The good news is that attacks typically unfold in a predictable way, so we can easily identify them when we know what to look for:
- First, a hacker pretends to be someone the victim trusts like a colleague, boss or authority figure and sends a fake email or message with a link to a bogus login page.
- The page looks like the real one (Google, Microsoft, Facebook, Instagram, etc.) The victim enters their username and passwords and are sent directly to the attacker.
- The attacker can then use the credentials, sell them, or launch further attacks like business email compromise or account takeover.
4) Data theft via viruses and malware

Malware is another prevalent method for stealing login credentials. This method installs malicious software like keyloggers, spyware, Trojans, and remote access tools to secretly steal login credentials and other sensitive data from a user's device.
Recent data shows malware is involved in a large share of data breaches, and security researchers have counted billions of malware attacks in a single year.
The infection process typically begins when users unknowingly download or install malicious software. This happens when you inadvertently do something that triggers the malware to be downloaded.
Common actions include clicking on an infected link in an email or visiting a malicious website. In other cases, hackers spread malware through peer-to-peer-file-sharing services and free software download bundles like embedding malicious computer code in a popular torrent or download.
Another technique is to load malware onto the firmware of a USB stick or flash drive. Then, when the USB stick is connected to another device, the malware will likely remain undetected because it's loaded onto the device's internal hardware.
Once the malware has been installed, it operates silently in the background, capturing keystrokes, monitoring user activity, and collecting login credentials and other sensitive information.
This data is then transmitted back to the attackers, who can use it for account takeovers, identity theft, or sell it on the dark web for profit.
5) Man in the middle (MitM) attacks

A Man-in-the-Middle attack happens when a hacker secretly intercepts and possibly alters communication between two parties (e.g., a user and a website), often to steal login credentials, session cookies, or sensitive data.
The attack typically unfolds when users connect to compromised or unsecured networks, such as public Wi-Fi hotspots.
In a common scenario, when you attempt to access your bank's website through a shared network, an attacker on the same network can redirect your traffic through their device instead of sending it directly to the bank's server. This redirection happens through network manipulation techniques that trick your device into routing data through the attacker's system.
Once positioned in this digital 'middle ground,' the attacker gains visibility into all data passing between you and the legitimate service. They can read your login credentials, modify transaction details, or capture session tokens that allow them to impersonate you later.
Research indicates that weak encryption practices play a big part in successful MitM attacks, which is why strong security protocols and avoiding unsecured networks matter for sensitive activities.
How organizations can protect against account takeovers
Even though there are many attack vectors we need to cover, there are effective methods of protection we can use to cover all the bases. Here are some of the most effective ways to protect your social media presence.
1) Use strong, complex passwords
Create strong, complex passwords and avoid reusing them to reduce the risk of unauthorized access to accounts and business systems and software. Many cyberattacks (like brute force attacks) rely on weak or reused passwords, having complex passwords make them much harder and less likely to succeed.
2) Enable multi-factor authentication
Multi-Factor Authentication (MFA) is one of the simplest and most effective ways to secure business accounts. It requires users to verify their identity with more than just a password (like a code from an authentication app, a text message, or a biometric scan).
Here's why MFA matters for your business:
- Even if a password is compromised, MFA adds multi-layered defense that prevents intruders from gaining access.
- MFA is perfect for defending against login theft via data breaches, brute force attacks, and malware that steals login credentials.
- Employees don't always follow strong password practices, MFA helps make up for that.
- Many data protection regulations and insurance policies now require MFA to be in place.
- While 2FA (two-factor authentication) is technically a subset of MFA (multi-factor authentication), it provides an effective solution for managing shared team accounts. If you implement team-based 2FA, your organization will be able to control which personnel receive access to login codes for sensitive accounts. There are different platforms that allow you to do just that. For example, Spikerz offers team-based 2FA that allows companies to manage access on a centralized dashboard. This ensures only authorized team members can access sensitive data while preventing unauthorized logins to shared social media accounts.
3) Train your employees to recognize phishing attacks
Phishing continues to be one of the biggest online threats to businesses worldwide. Cybercriminals often bypass technical security via targeting employees directly through deceptive messages.
Here's why employee training is a must:
- Employees who can identify and report phishing attempts help stop threats before they cause any damage.
- Most data breaches begin with a successful phishing email, training employees significantly reduces this risk.
- Training is perfect for helping employees recognize phishing direct messages, SMS messages (smishing), and deceptive comments sent through social media platforms.
- Preventing an attack is far less expensive and disruptive than dealing with the consequences.
- Regular training promotes awareness and helps make security a shared responsibility across the company.
4) Use account takeover protection to monitor your accounts
Account takeover (ATO) attacks are a growing threat to businesses, especially the ones with a strong online presence. For that reason, companies should do everything they can to ensure their accounts are protected.
Here's why using account takeover protection software is essential:
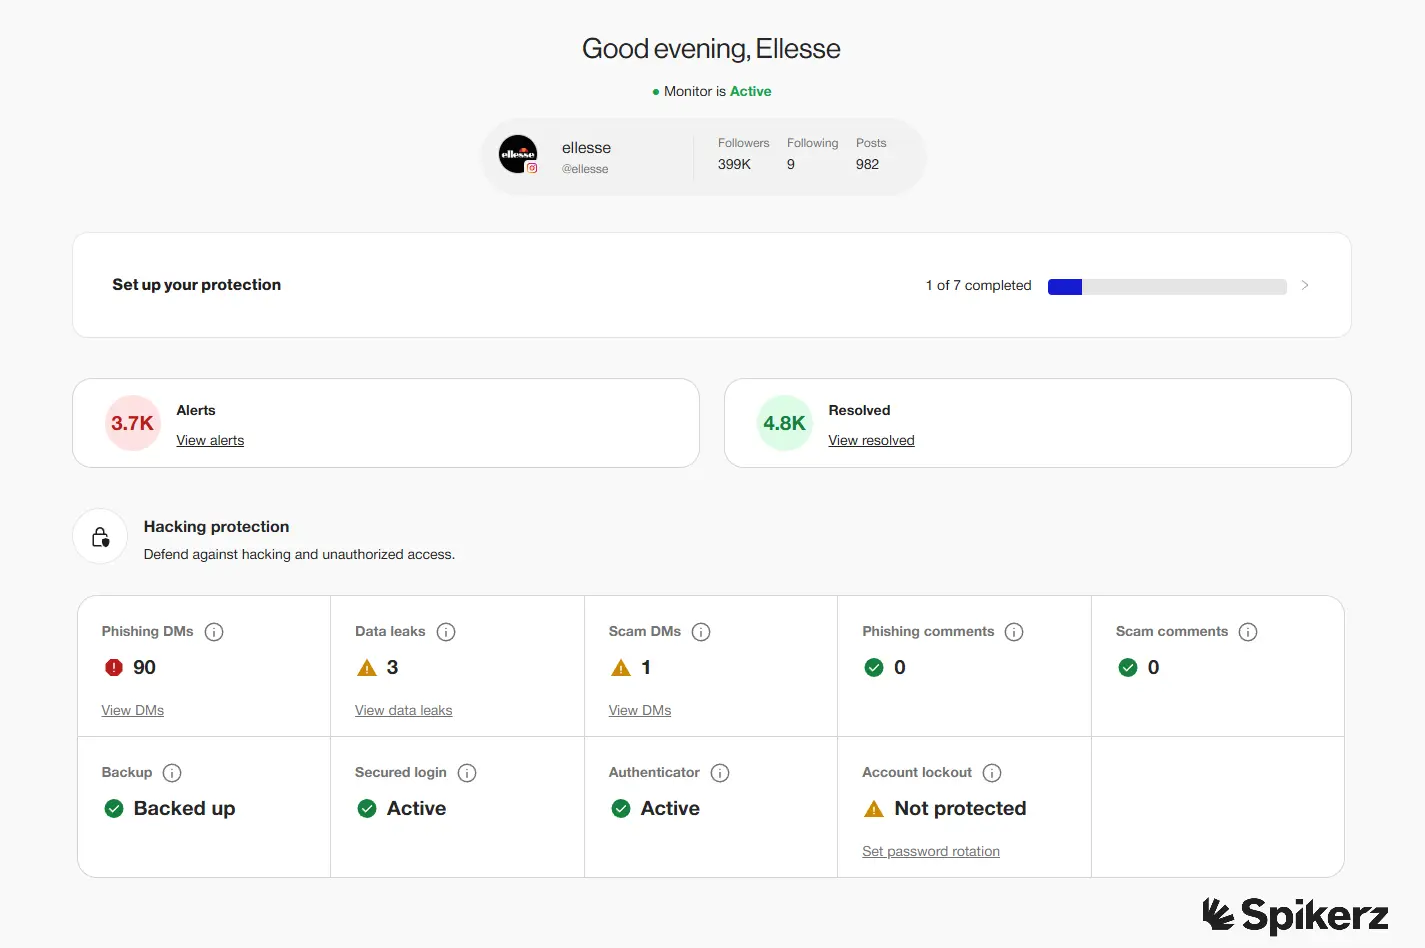
- It helps identify suspicious activity like unexpected logins, location changes, or device swaps.
- If a cyberattack manages to bypass other defenses, ATO protection is your safety net. It's perfect for identifying and stopping account breaches before they cause damage.
- Instead of waiting for human intervention, good ATO tools take immediate action to secure compromised accounts. Take Spikerz as an example. If a hacker breaches one of your social media accounts, Spikerz logs the intruder out, changes the password and alerts you. That quick response helps stop the damage before it spreads to your audience. For a full checklist, see our account takeover fraud prevention guide, or compare options in our list of the best account takeover protection software.
- Social media accounts are public-facing and often targeted by attackers. A breach here can damage your reputation quickly, ATO software ensures you stay in control.
5) Use antivirus software to protect local devices
Antivirus software is fundamental for any business that relies on computers, laptops, and local networks. It actively defends your devices from numerous threats that can compromise data, disrupt operations, or open the door to bigger attacks.
Here's why antivirus software is a must-have for businesses:
- It's perfect for protecting against all types of malware like viruses, ransomware, spyware, trojans, and more.
- Some antivirus solutions are advanced and help detect and block suspicious network activity, which reduces the risk of MitM attacks (hackers intercept data between your device and the web).
- Every endpoint is a potential entry point for attackers so antivirus software ensures employee devices (whether in-office or remote) are monitored and protected everyday, all day.
- Infected devices affect productivity or can lead to permanent data corruption, antivirus software catches threats early and minimizes disruption.
- Many data protection standards need antivirus software to be installed and actively maintained across all company devices.
Conclusion
Account takeovers are one of the most serious threats facing businesses online. The attacks we've covered, from data breaches and brute force cracking to phishing and malware, show how many ways hackers can compromise your accounts, and how quickly a takeover turns into fraud against your followers.
You aren't defenseless. Layered defenses make your accounts much harder to breach, and the best time to put them in place is before an attack happens.
Your social media accounts are too valuable to leave unprotected. Prevention costs far less than recovery, so start with the steps above. To see how Spikerz protects brand and executive accounts, book a consultation.
Sources
- FBI Internet Crime Complaint Center, "Account takeover fraud via impersonation of financial institution support", public service announcement I-112525-PSA, November 25, 2025. ic3.gov/PSA/2025/PSA251125
- Federal Trade Commission, "Reported losses to scams on social media eight times higher than in 2020", Data Spotlight, April 2026. ftc.gov
- FBI and CISA, "Threat actors deploy LummaC2 malware to exfiltrate sensitive data from organizations", joint cybersecurity advisory AA25-141B, May 21, 2025. ic3.gov/CSA/2025/250521-2.pdf